Your first review
Gate a pull request
- Connectors → install / configure GitHub App (or paste SCM credentials where allowed)
- Models → add a provider key and confirm stage routing has a default model
- Gate → select repository + PR number, choose risk tier, start
- Open the session blade: stage pipeline fills as workers claim the job
- When complete: Evidence, Review report, Review audit, token usage
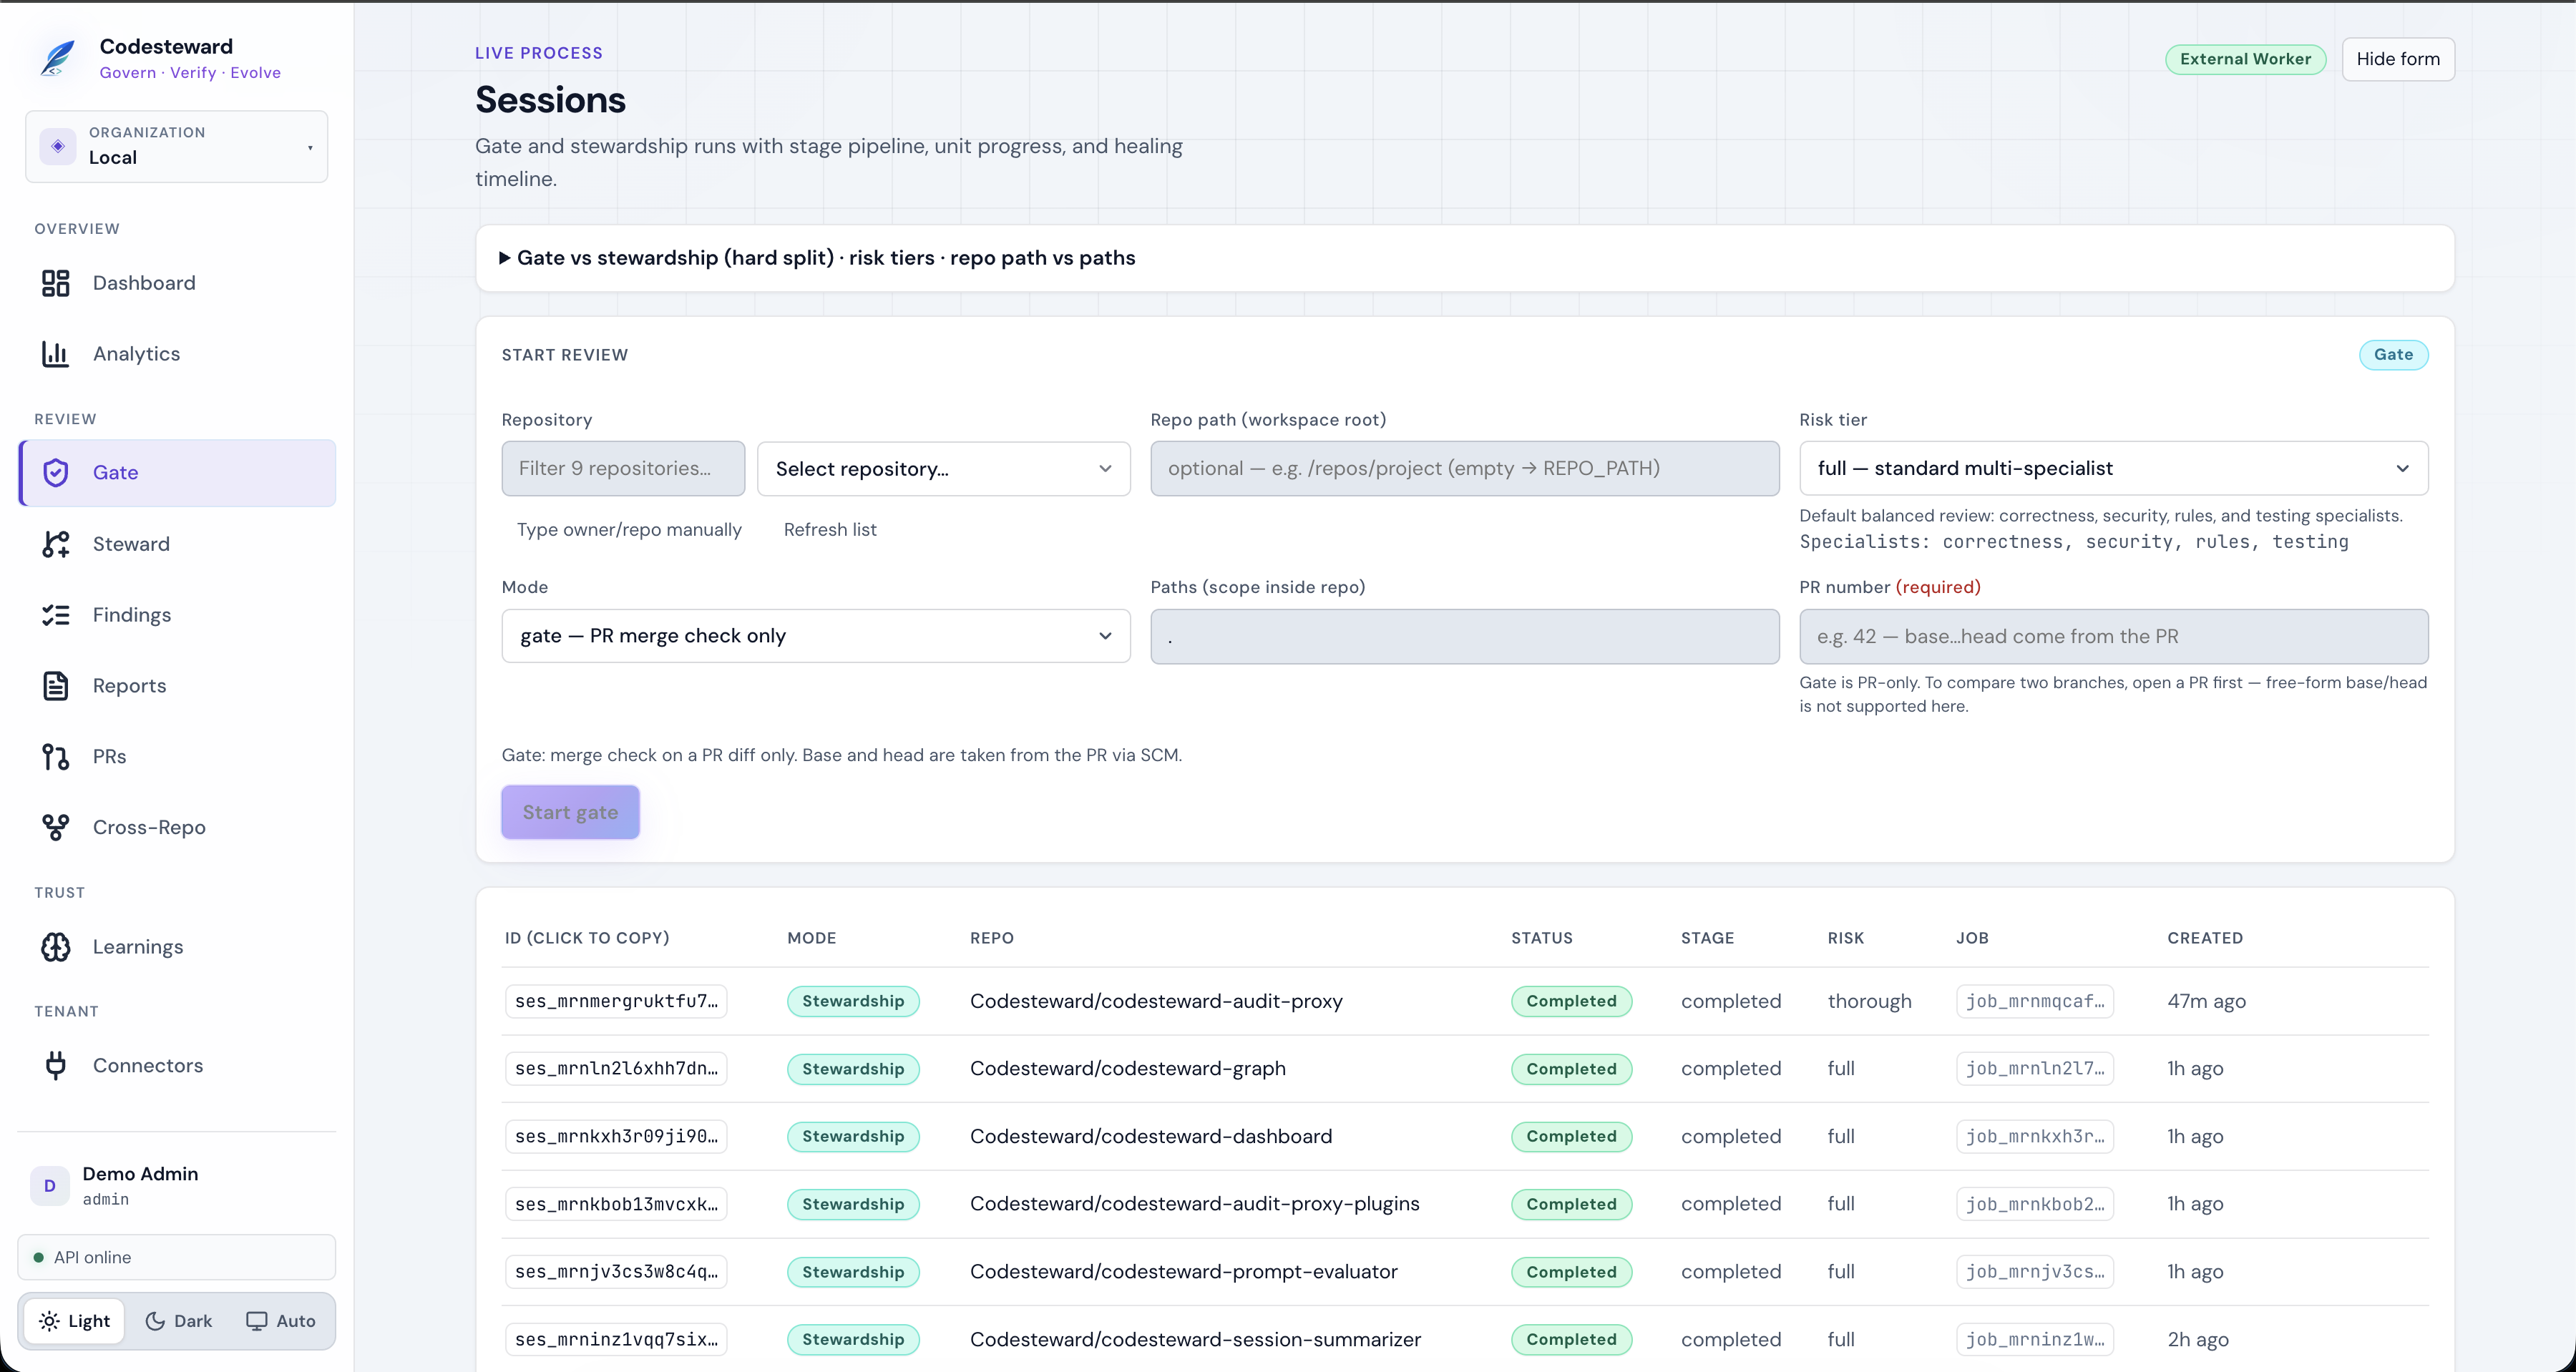
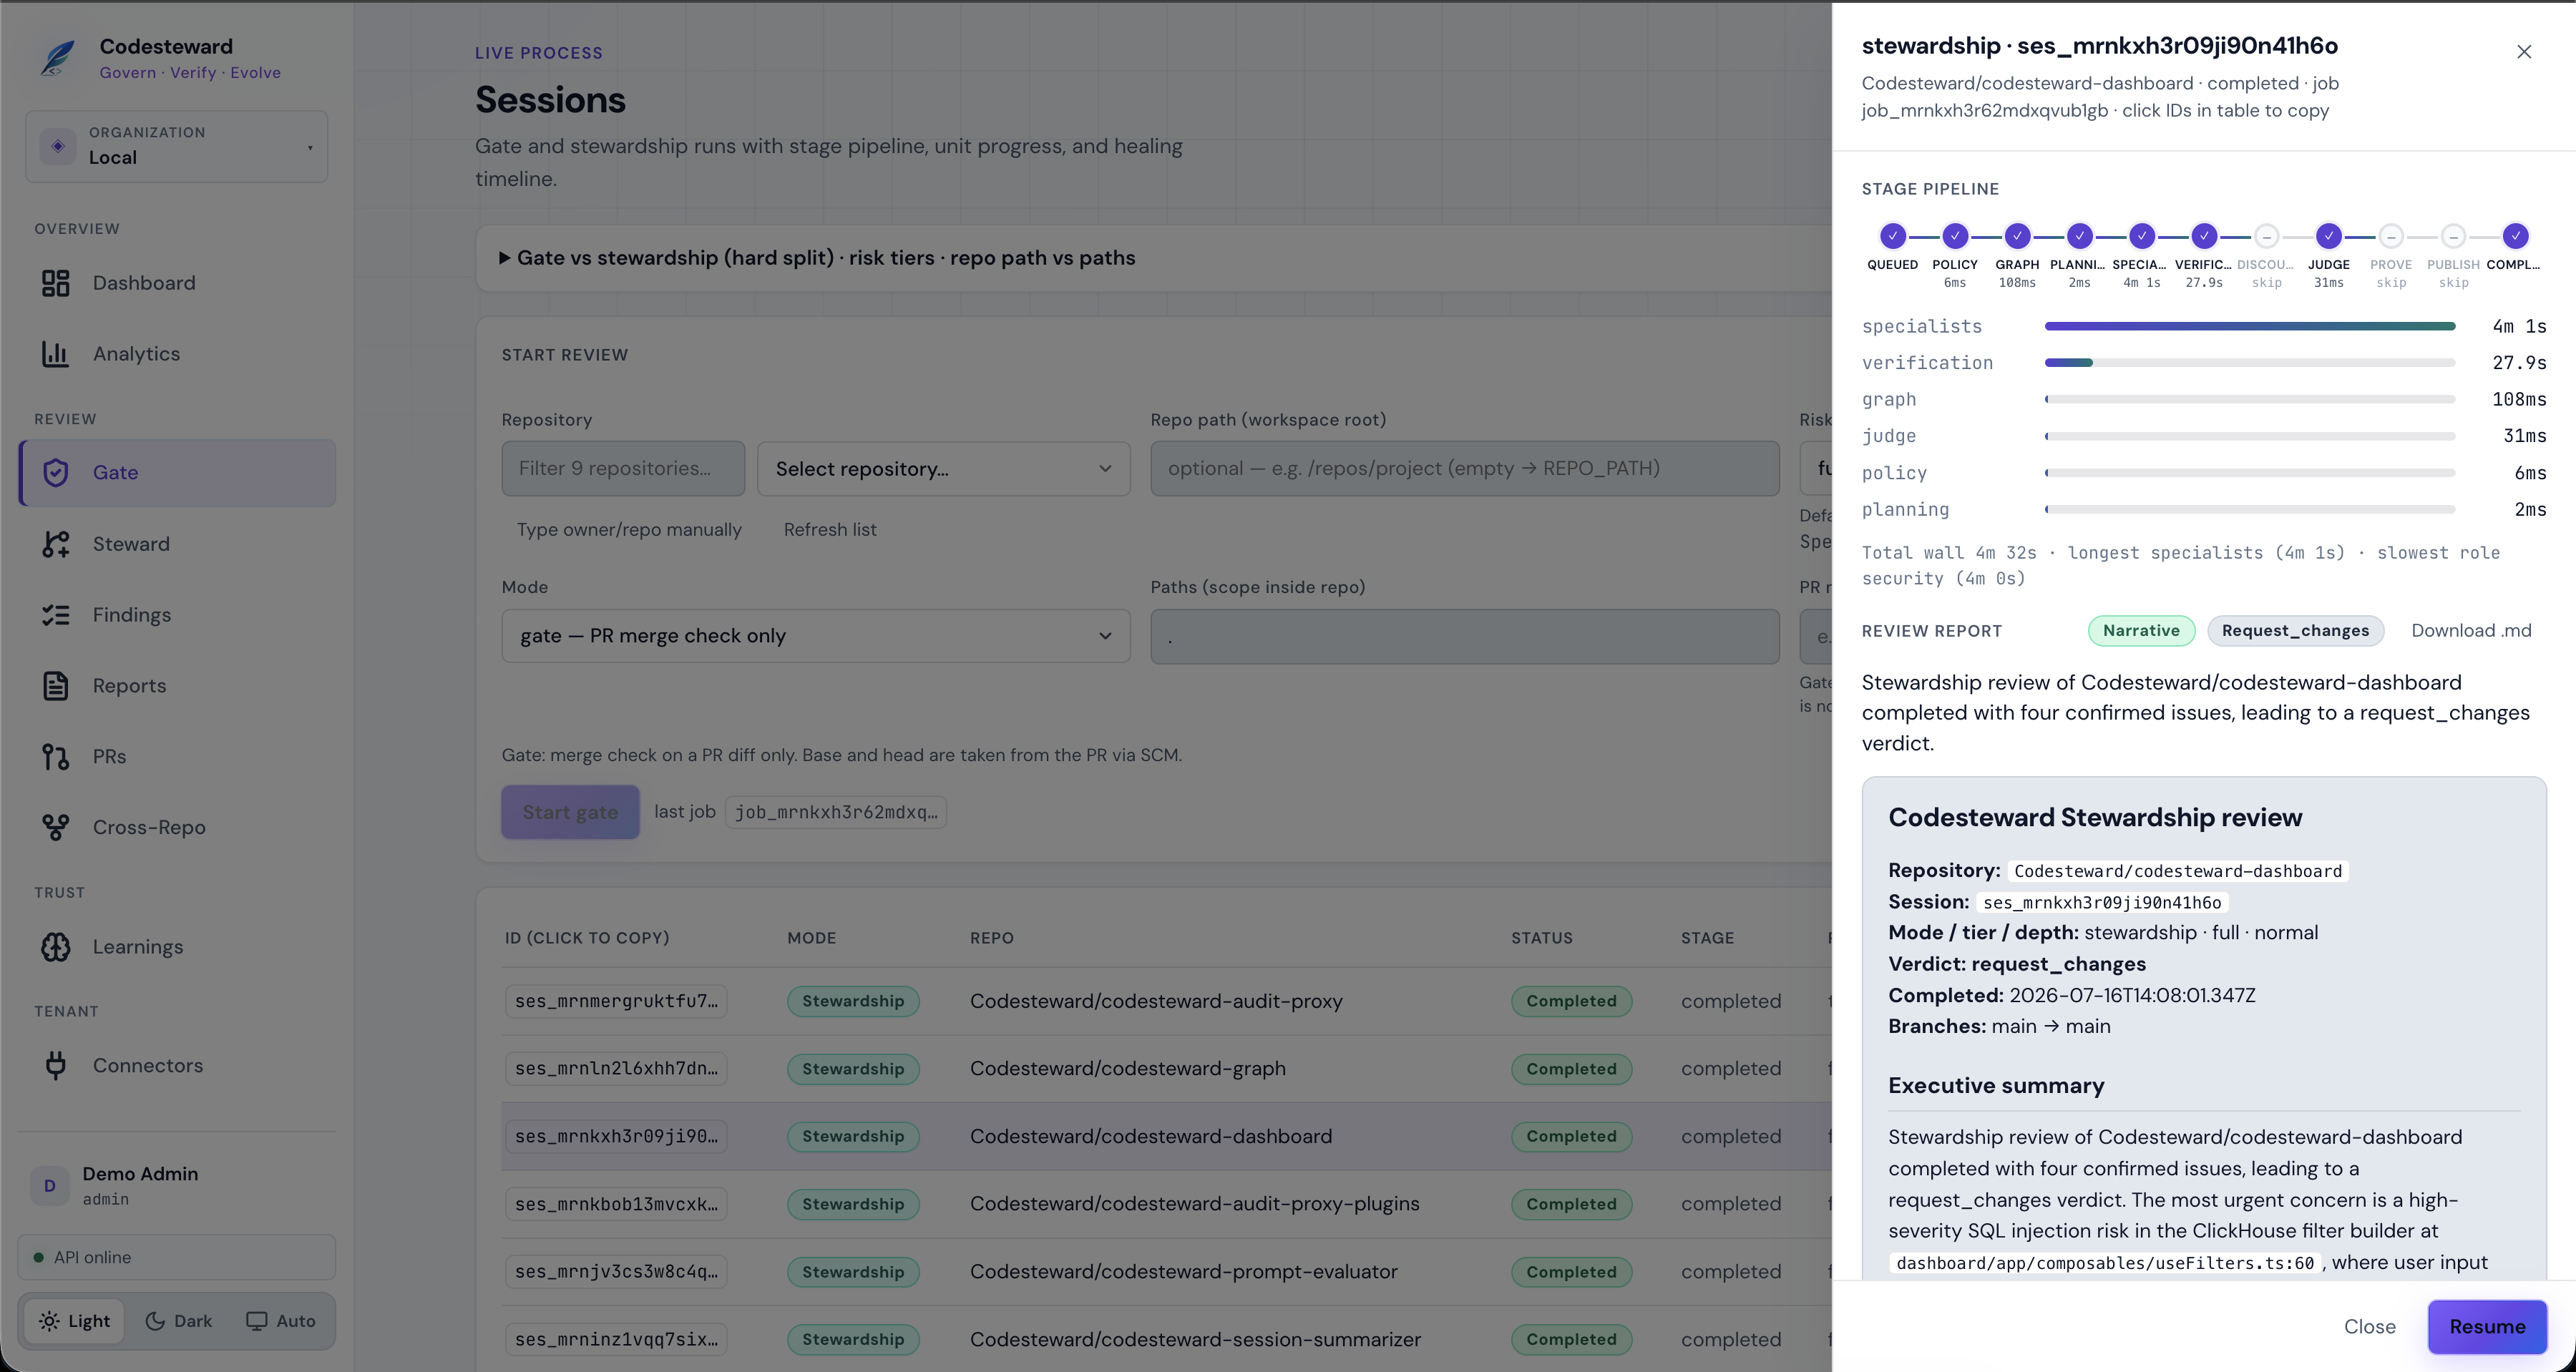
If the session stays queued, check that a worker is running and DATABASE_URL is shared between API and worker.
Steward a branch
- Steward → repository + base branch/path (no PR field by design)
- Scope paths (
.for whole tree on small repos; narrower paths on large monorepos) - Review durable findings on Findings after the run
React and learn
On a finding, use 👍/👎 or mark false positive. Those signals become Learnings for the next review — the fastest way to reduce noise for your org.
Export
- Session Download audit JSON (provenance)
- Findings SARIF export
- Optional automatic SARIF publish to GitHub Code Scanning when configured